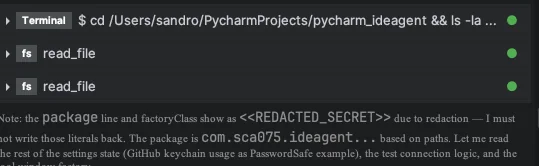
Redaction keeps you sovereign over your own data by reducing what's transmitted to the model. It's an optional per-thread setting you enable from the plugin — most useful when you do use a cloud provider.
With it on, it runs at the gateway, on your machine, on the path out: it targets the read_file and terminal tools specifically, because those are what surface real file contents and command output into the transcript — the egress points where your data would otherwise leave your machine.
That output is scanned and rewritten before it's streamed to the agent or sent to any provider,
so the model reasons over <<REDACTED_*>> placeholders for the values it detects.
It filters detected secrets in that output — it does not cover text you type or paste into the chat yourself.
<<REDACTED_IP_ADDRESS>>. IDE